How to Use Dig to Specify a DNS Server
Dig is a Linux tool that allows you to query nameservers. It also allows you to query specify nameservers for debugging.
On this page
Dig is a Linux tool standing for “Domain Information Groper” (yeah, it’s weird, but it is what it is). It’s used to get DNS information for a particular domain. Other tools do this, most notably “ping”, but dig allows users to go a step further and query specific DNS servers. This is useful for debugging, verifying propagation, and vetting the accuracy of the internal DNS records that your server might be using. The latter can be particularly complicated, so let’s see how we can use dig to solve the problem.
#How to Specify a DNS Server with Dig
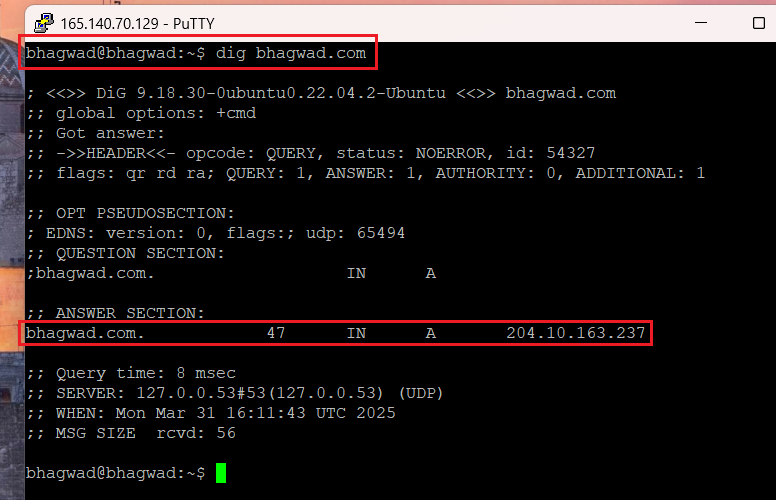
Here’s how to use the dig command to get the DNS address of a particular website. For these examples, I’ll use my site bhagwad.com. Here’s the format:
dig bhagwad.com
Here’s the output:

Using Dig with Default Nameservers
As you can see, dig has quite an involved output. The line that we’re interested in, however, is the “Answer Section”, where the domain resolves to 204.10.163.237. While this is useful, it doesn’t tell us which nameserver was called in order to arrive at this number. For all we know, dig could be using a locally stored resolved IP, and we’re getting outdated information.
Using the “+short” Parameter
One problem with the dig command is the sheer volume of the output that we receive. All of it is useful, and for debugging purposes, you need to see every detail. But if you just want a single answer, or if you’re using dig in scripts that require a single response, then you can use the “+short” parameter to limit the output and give you just the answer like this:
dig +short bhagwad.com
This gives the following output:

Dig with Short
As you can see, you get just the answer, and nothing more. If you’re using dig in a script as part of a function where the response feeds into another process, then you should use the “+short” parameter, instead of parsing and extracting the output yourself.
Specifying the Nameservers
To ensure that we’re receiving the latest information, in case you’ve changed your DNS information recently, we can use dig to specify the actual nameserver to query. For example, let’s use two popular nameserver services – Google and Cloudflare. These are the two commands I’m using:
dig @1.1.1.1 bhagwad.com
dig @8.8.8.8 bhagwad.com
And here’s the output:

Dig with Nameservers
As you can see, I’m querying two different DNS servers to resolve my domain name. In this case, they’re both giving different answers because of the way I’ve set up my DNS configuration with QUIC.cloud and Cloudflare, and there’s some configuration with a CNAME record, but you don’t need to worry about that. It’s useful to show how different nameservers can return different results!
#Contrast Between Dig and Ping
Chances are that the tool you most often use to get the IP address of a domain is “ping”. It’s a more well-known command and gets the job done. For example:
ping bhagwad.com
This shows the following:

DNS Resolution with Ping
This familiar output shows you what happens when your server tries to connect with a domain. However, the DNS is resolved using the default DNS server that’s configured with your system, and it might even be a locally cached DNS response that hasn’t changed recently, and thus runs the risk of being outright wrong. More importantly, ping doesn’t allow you to change the DNS server that it uses to query the response, so you have no way of debugging a possible DNS error.
For regular site responsiveness, ping is a great tool – well-known and elegant. But for DNS debugging purposes, it’s pretty useless.
#Querying Authoritative Nameservers with Dig
Querying specific nameservers for DNS resolution is well and good, but how do you know which nameservers to query? Because of the way the DNS architecture works, the information is spread out across several nameservers. Out of all of them, one nameserver is called “authoritative”. This is the set of nameservers that you usually specify on the configuration page of your domain registrar for your domain. Domain registrars usually come with their own nameserver systems, but they allow you to change the nameservers to something else. Except for Cloudflare. When you register a domain with Cloudflare, they force you to use their nameservers.
The authoritative nameserver acts as the gold standard for domain name resolution. A process known as DNS propagation ensures that IP changes at the authoritative nameserver make their way to all the other nameservers on the Internet, including those run by Google and Cloudflare. So in general, querying any DNS servers should give you the same result as querying the authoritative nameserver. This is complicated by location-based DNS and load-balancing systems, but the general idea is correct.
Checking Propagation
However, problems can occur when you’re not sure if your DNS changes are being propagated. For example, let’s say you’ve switched hosting providers and now the IP address for your site is different from what it used to be. So you make the change to the IP address on your registrar’s nameservers. Now you need to wait for all the propagations to finish. If you’re facing errors, you might find that the changes haven’t been propagated. But you suspect that maybe the old IP is still showing up on even the authoritative nameserver. How do you verify that it’s working?
To do this with Dig, first, we need to get the names of our authoritative servers. So we use the following command:
dig bhagwad.com NS
This gives:

Getting the Authoritative Nameserver
You can see that my current authoritative nameservers belong to Cloudflare. We can now use the above nameservers to query the IP address for the site:
dig @jason.ns.cloudflare.com +short bhagwad.com
dig @vita.ns.cloudflare.com +short bhagwad.com
Ideally, both of these queries should give you the same answer, since they’re both authoritative. And that’s what we see:

Querying Authoritative Nameservers
So everything’s working as intended. At this point, if you see the expected new IP addresses, there’s nothing you can do but wait for them to propagate.
#Combining Dig with Other Commands
While dig is useful on its own, you can also use it while combining its output with other commands. For example, if you want to ping a website to see if it’s working, and want to use a specific DNS server to resolve the IP address, you can combine the “ping” and “dig” commands into one like this:
ping $(dig +short @1.1.1.1 bhagwad.com)
You can also use dig with a command like “grep” to extract other records and filter the output so that you get clean responses. For example:
dig wp-tweaks.com MX +short | grep -v '^0 '
This generates the following output:

MX Records with Dig
The “grep” command above, filters out mail records with a priority of 0 – if they exist, they’re used for special purposes.
Dig can even be on the receiving end of a piping command. For example, let’s say you have a text file with a list of domains and you want to find the “A” records for each of them. The following command does it quickly and neatly:
cat domains.txt | xargs -n 1 dig +short -A
This takes the domains in the file one by one and feeds them into dig, which will then output the “A” records of each.
#Conclusion
As you can see, you can use dig to specify DNS servers to query when resolving a domain name. But it also goes far beyond that. If you’ve only been using “ping” so far to get the IP address of a domain, then it’s time you added “dig” to your repository of tools!